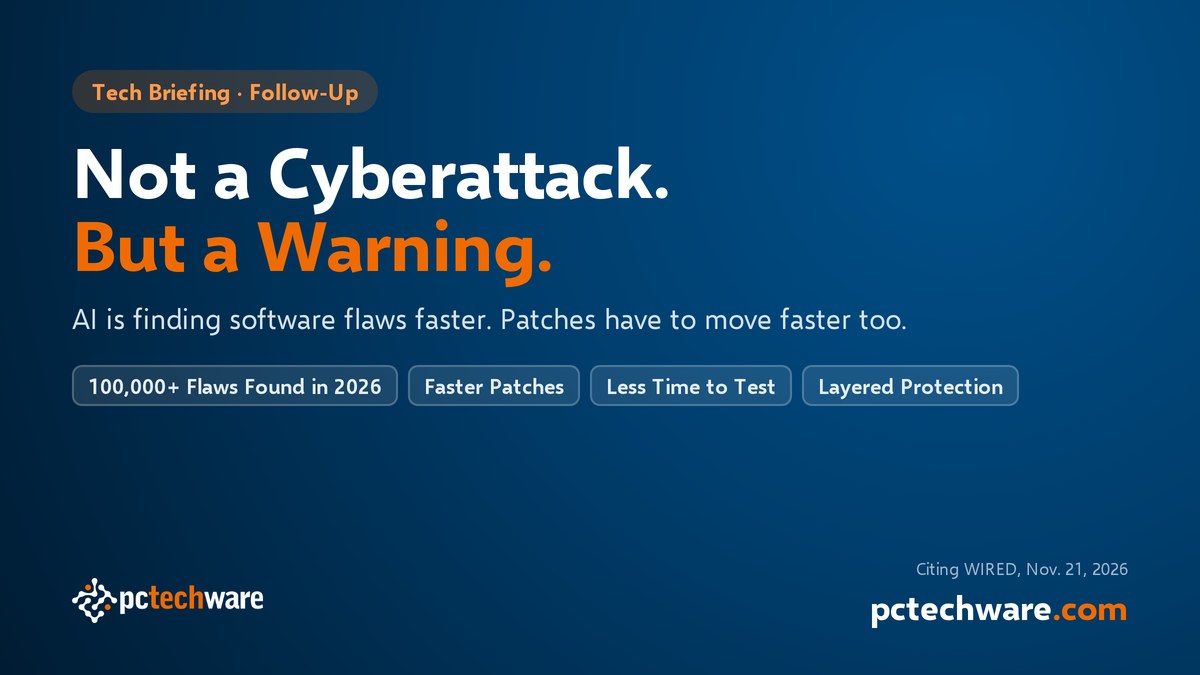
Last week I wrote about 13 tech outages in seven days and the question our service desk kept hearing: is this a cyberattack? Outage by outage, the answer was no. It was a perfect storm of ordinary failures landing in the same week: a software update, a backup test, a hidden bug, a busy server, routine maintenance.
On November 21, WIRED published a piece by Lily Hay Newman and Matt Burgess titled The Outages Are Just Getting Started. [1] It opens with the same conclusion we reached, then goes a step further and explains why weeks like that one may become more common. I think it is worth five minutes of every business owner's time, so here is what it says and what it means for you.
First, It Was Not Hacking
WIRED put it plainly: the incidents were "definitely not caused by some sort of coordinated AI hacking spree and, taken individually, they all seem to have routine explanations." [1] Senator Mark Warner, vice chairman of the Senate Intelligence Committee, said the same in a statement on November 17: "At this point, there is no indication that these incidents are the result of a cyberattack, foreign interference, or some coordinated effort." [2]
Look at the causes WIRED lists. Microsoft's 365 outage came from a flawed update in its infrastructure, made worse by other network failures. Apple said its problems were related to an internal update. And WIRED reports that officials said the NSA's internal communication outage was due to botched patching after October's critical PHP updates. [1] (Our earlier post quoted the NSA's November 17 statement, which described the problem as temporary degradation during scheduled routine maintenance.) Notice the common thread. These were not break-ins. All three trace back to updates.
What Is Changing: AI Speeds Everything Up
Here is the part that is new. According to WIRED, AI-assisted tools have "unleashed a torrent of software bugs." Attackers then use AI to exploit those flaws faster, which puts more pressure than ever on organizations to patch quickly. WIRED says researchers and practitioners have told its reporters again and again that AI's biggest impact is that it speeds everything up. [1]
The numbers are hard to ignore. WIRED reports that the number of vulnerabilities found in 2026 has passed 100,000, compared with around 25,000 in 2022, the last year before large language models, the technology behind AI chatbots, went mainstream. [1] Each of those is a CVE, a public ID number given to a known software flaw. The Register reported the count crossed 100,000 on November 13, more than double all of 2025, [4] and Black Kite's research team counted 100,009 published CVEs as of November 18, 2.1 times the 2025 total. [5]
Senator Warner described the result as "putting tremendous strain on systems that weren't built to handle that pace of change." [1][2] Microsoft CEO Satya Nadella, speaking at The New York Times DealBook Summit, said more instability could be coming because a "patch needs to go instantly from being available to being patched in production because it's being exploited in the wild." [1][3] In plain English: once a flaw is public, criminals start using it right away, so the fix has to go onto the live systems people depend on just as fast.
That leaves less time to test. Joe Slowik, director of threat research and cyber engineering at Dataminr, told WIRED that a couple of years ago, when a vendor released a patch for a nasty bug, "You might have some time to do some validation and apply it." Now, he said, "that may not even be an option, because we're talking about turnaround times that completely defeat the ability to do patch verification." [1] AI helps the defenders too, but it does not replace people. "AI can help, but people still need to understand what went wrong, check that the patch addresses the cause, and look for similar issues elsewhere," Lea Schönherr of the CISPA Helmholtz Center for Information Security told WIRED. [1]
WIRED also points to tech debt: years of cut corners and skipped upgrades. Researchers told WIRED that organizations used to gamble with out-of-date systems and missing safeguards and usually avoid the worst consequences. [1] My read is that the odds on that gamble are getting worse.
Put it all together and the chain is simple. Flaws are found faster. Attackers move faster. Patches have to go out faster, with less time to test them. And when patches move that fast, some of them will break things. That is the technical landscape now, and I do not expect it to slow down soon.
Some Perspective: Not Every Flaw Is a Fire
Before anyone panics, WIRED adds important nuance. "The number of vulnerabilities has certainly exploded, but the number of vulnerabilities that you need to care about has remained somewhat constant," Slowik said. "The caveat is that the pace at which they're being used or weaponized has increased dramatically." [1]
WIRED notes that only about 300 vulnerabilities have been added this year to the federal Cybersecurity and Infrastructure Security Agency's (CISA) catalog of flaws known to be exploited by attackers. [1] We checked CISA's own catalog data: as of November 20, 306 entries had been added in 2026. [6] VulnCheck, which keeps its own list, puts the figure at about 1,500, which WIRED notes is still only 1.5 percent of all the bugs found this year. [1]
Cloudflare CEO Matthew Prince told WIRED that "it's going to feel like the sky is falling for two years," though he expects AI to eventually help defenders get ahead, so that "the background noise will actually tick down quite a bit." [1] So the job is not to chase every headline. It is to spot the small number of flaws that matter and move quickly on those.
Yes, We Know the Updates Are Annoying
I want to be honest about this, because our clients are honest with us. Frequent updates and forced restarts are frustrating. The restart prompt always seems to show up in the middle of something important. We hear it, and we understand. But this is how it has become, and based on everything above, it is not going away.
Why We Still Push Updates Through
When we push an update and ask you to restart, it is not because we enjoy interrupting your day. It is because if an update were skipped and a breach followed, we would feel accountable. Every business makes its own choices, and sometimes a client decides to hold off on an update or asks us not to enforce one. That is your decision to make, our agreements respect it, and nobody can be forced. But as your IT provider and trusted advisor, we carry a real responsibility to protect you. So we will always recommend updating promptly, and we will tell you plainly when we think waiting carries risk.
Updates Are One Small Piece of Security
As important as they are, updates are only a small part of the picture. In managed IT we do not plan around whether a breach will happen. We plan for when, not because we expect the worst, but because planning for it is what keeps a bad day small. That planning is layered:
- Control the attack surface. Every device, account and connection that can be reached from outside is a possible door. Fewer doors, better watched, means fewer ways in.
- Backups you can count on. Verified, so we know they restore. Resilient and immutable, meaning they cannot be changed or deleted, even by someone holding a stolen password. And copies held by a third party, outside your main systems.
- Redundant systems and fail-safes. So one failure does not stop the whole business.
- Multiple layers of protection. A security operations center (SOC), a team that watches for warning signs. A SIEM, which gathers security logs in one place so unusual activity stands out. EDR, endpoint detection and response, which spots and stops suspicious behavior on each computer. And levels of passwords and levels of access, so each person can reach only what their job requires.
- Procedures. Written plans, so everyone knows what to do when something goes wrong.
Recovery Should Be an Organized Event
With those layers in place, a recovery becomes an organized, composed event instead of a hair-on-fire scramble. That is the difference preparation makes.
Much of what we do in IT is exactly that: preparation. It is also why you rarely hear about it. When the plan works, there is no story to tell. Last week's outages showed the same thing on a larger scale: behind every headline was a team that found the problem, fixed it and told the public what they knew.
So if the headlines have left you uneasy, here is my message. The outages were not an attack. The pace of change is real. And we are prepared for it. If you would like to talk through how ready your business is, schedule a conversation with our team.
Read WIRED's full article: The Outages Are Just Getting Started. [1]
Sources
- WIRED, Lily Hay Newman and Matt Burgess, The Outages Are Just Getting Started (Kernel Panic newsletter), November 21, 2026. www.wired.com
- Office of U.S. Sen. Mark R. Warner, Senate Intel Vice Chair Warner Statement on Network Outages, November 17, 2026. www.warner.senate.gov
- TechCrunch, Satya Nadella at The New York Times DealBook Summit, November 18, 2026. techcrunch.com
- The Register, This year's bug count just passed 100K, November 13, 2026. www.theregister.com
- Black Kite Research Group, 2026 CVE Report: Vulnerabilities Hit 100,000, November 18, 2026. blackkite.com
- CISA, Known Exploited Vulnerabilities Catalog data feed, catalog version 2026.11.20. www.cisa.gov
Russell leads PC Techware and its cybersecurity and compliance practice, including CMMC and NIST readiness.
Connect on LinkedIn