Request a Consultation
The path to a more secure, efficient business starts with expert consultation. Send us your information, and we'll be in touch to schedule an appointment at your convenience.
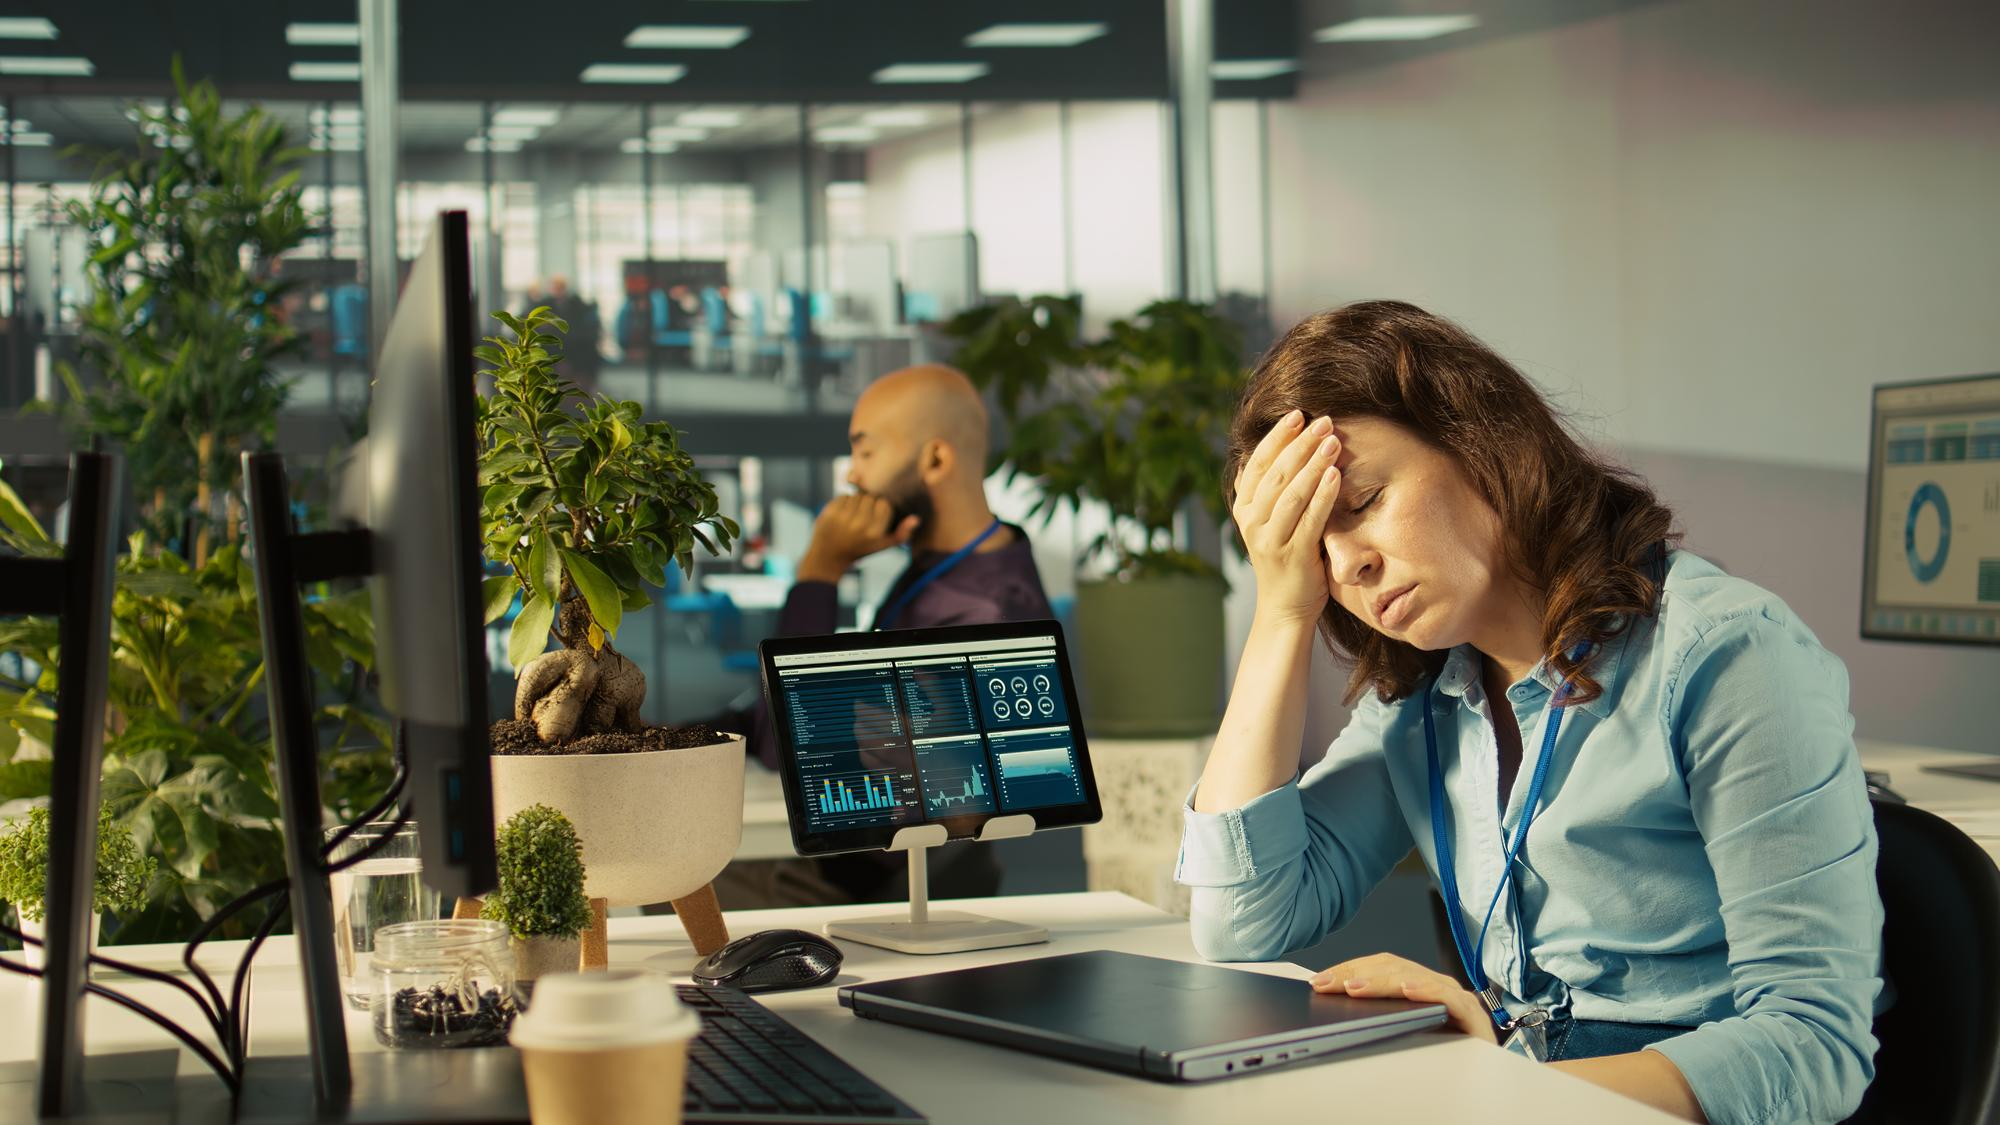


Cybersecurity discussions often focus on advanced threats such as ransomware, malware, and sophisticated hacking techniques. While these threats are serious, many successful cyberattacks begin with a much simpler vulnerability: human error. In CPA offices, where employees regularly handle confidential financial records, tax documents, payroll information, and sensitive client communications, a single mistake can lead to significant security consequences.
As cybercriminals increasingly target accounting firms, understanding the role human error plays in cybersecurity incidents has become essential. Organizations that invest in employee education, security awareness, and proactive risk management are better positioned to reduce vulnerabilities and protect client data.
Human error remains one of the most common causes of cybersecurity incidents across all industries. Employees interact with emails, applications, files, and client information daily, creating numerous opportunities for mistakes that attackers can exploit.
Cybercriminals often target people rather than technology because employees can be easier to manipulate than security systems. Attackers use social engineering tactics to convince users to click malicious links, share credentials, transfer funds, or provide confidential information.
Even organizations with strong technical defenses can become vulnerable when employees unknowingly bypass security controls. Human behavior continues to play a critical role in determining the effectiveness of any cybersecurity strategy.
A single employee error can create substantial financial and operational consequences. Mistakes such as sending confidential information to the wrong recipient, clicking a phishing link, or using weak passwords can result in unauthorized access to sensitive systems.
For CPA firms, these incidents can disrupt client services, damage professional reputations, and trigger regulatory concerns. Recovery efforts often require significant time and resources, making prevention a far more effective strategy than remediation.
Many data breaches occur because employees unknowingly provide attackers with access to systems and information. Cybercriminals frequently exploit trust, urgency, and routine business processes to deceive users into taking actions that compromise security.
Human error can occur at any level of an organization, highlighting the importance of ongoing education and awareness initiatives that reach every employee.
CPA offices face unique cybersecurity challenges due to the volume of sensitive information they manage and the frequency of client interactions.
Phishing attacks remain one of the most successful methods used by cybercriminals. These emails often appear to come from trusted clients, government agencies, software vendors, or financial institutions.
Attackers design phishing messages to create urgency and encourage immediate action. Employees who click malicious links or download infected attachments may unknowingly provide attackers with access to internal systems and confidential information.
Because accounting professionals frequently receive financial documents and client communications, distinguishing legitimate messages from fraudulent ones can be challenging without proper training.
Password-related vulnerabilities continue to contribute to many cybersecurity incidents. Employees often reuse passwords across multiple accounts or create simple passwords that are easy to remember but also easy for attackers to guess.
When compromised credentials become available through data breaches or phishing attacks, cybercriminals frequently test those credentials across multiple platforms. Reused passwords significantly increase the likelihood of unauthorized access.
Strong password policies combined with multi-factor authentication can substantially reduce these risks.
CPA firms routinely process confidential financial information, tax records, payroll data, and personal identification details. Mishandling this information through improper sharing, unsecured storage, or accidental disclosure can expose organizations to significant security and compliance risks.
Employees should understand proper procedures for transmitting, storing, and accessing sensitive information to minimize the risk of accidental exposure.
Organizations often establish cybersecurity policies to protect systems and data. However, these policies are only effective when consistently followed.
Employees who bypass security procedures for convenience may unintentionally create vulnerabilities that attackers can exploit. Consistent enforcement and regular education help reinforce the importance of compliance with established security standards.
Human mistakes often serve as the initial entry point for broader cyberattacks.
Not all security incidents involve malicious intent. Employees may accidentally expose sensitive information through misconfigured settings, improper file sharing, or accidental disclosures.
These incidents can still have serious consequences even when no malicious activity is involved. Organizations must implement safeguards that reduce the likelihood of accidental exposure while maintaining operational efficiency.
Social engineering attacks exploit human psychology rather than technical vulnerabilities. Attackers use trust, fear, urgency, curiosity, and authority to influence employee behavior.
Examples include fraudulent requests from individuals posing as executives, clients, government officials, or technology vendors. Effective awareness training helps employees recognize these tactics before they lead to security incidents.
Compromised credentials remain one of the most common causes of unauthorized access. Once attackers obtain valid login information, they can often move through systems undetected.
Protecting user credentials requires a combination of employee education, strong authentication controls, and continuous monitoring to identify suspicious activity.
Certain characteristics of CPA firms make them particularly attractive targets for cybercriminals.
Accounting firms manage large amounts of confidential information on behalf of clients. This information often includes financial records, tax filings, payroll data, banking information, and corporate reports.
The concentration of valuable information creates significant incentives for cybercriminals seeking financial gain or data theft opportunities.
Many organizations strengthen protection efforts by partnering with providers offering managed IT services for CPA environments that understand the unique security requirements of accounting firms.
CPA offices regularly exchange documents, financial statements, tax forms, and confidential information through email and file-sharing platforms.
The high volume of communications creates additional opportunities for phishing attacks, fraudulent requests, and accidental data exposure.
Accounting professionals often operate under strict deadlines, particularly during tax season and financial reporting periods. Increased workloads can reduce the time available to carefully evaluate emails, attachments, and requests.
Cybercriminals frequently exploit these busy periods because employees may be more likely to make mistakes when working under pressure.
Employee education remains one of the most effective methods for reducing human-related cybersecurity risks.
Security awareness training helps employees understand current threats, recognize suspicious activity, and follow best practices when handling sensitive information.
Training should address real-world scenarios relevant to accounting professionals and provide practical guidance for identifying common attack techniques.
Employees need clear guidance regarding acceptable technology use, password management, data handling, remote work practices, and incident reporting requirements.
Well-documented procedures create consistency and reduce uncertainty when employees encounter potential security issues.
Cybersecurity should be viewed as a shared responsibility rather than solely an IT function. Every employee contributes to organizational security through daily decisions and actions.
Organizations often enhance internal capabilities through co-managed IT services and support, which help reinforce security initiatives and provide additional expertise.
Practical exercises help employees apply cybersecurity concepts in realistic situations.
Phishing simulations involve sending realistic but controlled phishing emails to employees. These exercises allow organizations to evaluate how staff respond to suspicious messages without exposing systems to actual threats.
The results provide valuable insights into employee readiness and areas requiring additional training.
Simulation results help organizations identify trends, knowledge gaps, and departments that may require additional support.
Regular assessments provide measurable data that can be used to improve training effectiveness over time.
Employees who fall for simulated phishing attacks should receive constructive feedback and targeted education. The goal is continuous improvement rather than punishment.
Organizations that encourage learning create stronger long-term security outcomes.
Security awareness should extend beyond annual training sessions.
Employees should learn how to identify common warning signs, including unexpected attachments, unusual requests, suspicious links, and urgent demands for action.
Consistent awareness helps reduce the likelihood of successful phishing attacks.
Strong passwords, password managers, and multi-factor authentication significantly improve account security.
Employees should understand why these controls are important and how to use them effectively.
Protecting client information requires secure storage, controlled access, encrypted communications, and responsible sharing practices.
Employees should understand both organizational requirements and regulatory expectations regarding data protection.
Human resources and compliance teams play an important role in supporting cybersecurity initiatives.
New employees should receive cybersecurity training as part of the onboarding process. Early education establishes expectations and helps create a strong security culture from the beginning.
Cybersecurity training should be continuous rather than a one-time event. Regular updates help employees stay informed about evolving threats and changing compliance requirements.
Maintaining visibility into organizational technology assets is essential for both security and compliance. Professional IT asset management services can help organizations track hardware, software, and technology resources more effectively.
Long-term cybersecurity success depends on organizational culture.
Leadership teams set the tone for cybersecurity priorities. When executives actively support security initiatives, employees are more likely to take cybersecurity responsibilities seriously.
Employees should feel comfortable reporting suspicious activity without fear of blame. Early reporting allows organizations to investigate potential threats before they escalate.
Cybersecurity is an ongoing process rather than a one-time project. Continuous learning, regular assessments, and evolving training programs help organizations adapt to changing threats.
Human error remains one of the most significant cybersecurity risks facing CPA offices today. While technology plays an important role in protecting systems and data, employee actions often determine whether attacks succeed or fail. By investing in cybersecurity awareness, phishing simulations, clear policies, ongoing education, and proactive technology management, CPA firms can significantly reduce risk and strengthen their overall security posture. Building a culture where every employee understands their role in cybersecurity is one of the most effective ways to protect sensitive financial information and maintain client trust.

Download our free FTC Safeguards Rule Compliance Checklist to help you navigate to a more secure and confident future.

Request your FREE Dark Web Report and see if your company is already compromised.

Ready to secure and improve your IT? Reach out for your free consultation today.

Technology has become the backbone of every successful small business. From managing customer information and business applications to securing sensitive data...
Cloud technology has transformed the way businesses store data, collaborate with teams, and access applications from anywhere. While cloud solutions offer...
Technology has become one of the most valuable assets for modern businesses. From managing daily operations to protecting sensitive business information,...

Business technology looks very diferent from one industry to the next. Explore the unique technology challenges and solutions faced businesses in each industry below.

Learn day-to-day tips anyone can use to improve their cybersecurity posture and get more out of technology.

Learn about the cybersecurity challenges faced by SMBs and how they're adapting to today's IT concerns.

Learn how legal teams are mounting a resilient defense against data breaches and compliance concerns.

Learn how financial institutions are managing sensitive account data in today's hyper-connected world.

Learn how businesses are adapting to the growing need for technology in the construction industry.

Contact our security experts today to schedule a cybersecurity risk assessment and get a clear picture of your business’ vulerabilities.

 +1-706-389-0580